The Ultimate Guide to Food Delivery Fraud: Types, Detection & Prevention Strategies
Share this article
The food delivery industry has grown into a trillion-dollar market and wherever money flows at scale, fraud follows. From fake driver accounts and GPS spoofing to chargeback abuse and bot-driven ghost orders, food delivery fraud is costing platforms millions and eroding user trust.
This guide breaks down every major type of food delivery fraud, how it works, and the fraud detection strategies that actually stop it.
What Is Food Delivery Fraud?
Food delivery fraud refers to any deliberate attempt to exploit a food delivery platform - by customers, delivery drivers, or organized fraud rings - for financial gain or unfair advantage.
It can take many forms: a customer filing a false refund claim, a driver spoofing their GPS to fake a delivery, or a fraudster spinning up thousands of fake accounts to drain promotional budgets. What these attacks share is that they exploit the trust and automation that make modern food delivery platforms work.
For platforms and restaurant operators, the impact is direct - lost revenue, damaged reputation, and rising operational costs.
Why Food Delivery Fraud Is Increasing in 2026
Food delivery platforms have scaled faster than their fraud defenses. A few structural reasons explain why fraud rates keep climbing.
Transaction volumes give fraudsters cover — a few hundred fake accounts disappear inside millions of daily orders
Fraud tools are now accessible to anyone — app cloners, GPS spoofers, and bot frameworks require little technical skill to operate
Generous promotions are a magnet — first-order discounts and driver sign-up bonuses are the most frequently abused features on any platform
The multi-sided attack surface multiplies risk — fraud can enter through customers, drivers, or restaurants, often at the same time
Platforms that rely on manual reviews or rule-based systems are finding it increasingly difficult to keep up. The shift toward real-time fraud detection in food delivery is a baseline requirement for running a sustainable platform.
Common Types of Food Delivery Fraud
Fraud in food delivery does not follow a single pattern. It shows up across every layer of the platform, from how accounts are created to how orders are fulfilled and paid for. Here are the six most common types platforms deal with today.
Promo and Coupon Abuse
Promotional budgets are one of the most targeted areas in food delivery fraud. Fraudsters create large numbers of fake accounts to repeatedly claim first-order discounts, referral bonuses, and seasonal offers that are intended for new or genuine users.
A single bad actor with access to an app cloner and a device emulator can generate hundreds of accounts from one device, cycling through promotions at scale. For platforms running aggressive growth campaigns, this can translate into hundreds of thousands of dollars in unearned discounts.
Chargeback Fraud & Refund Abuse
These are two related problems.
Chargeback fraud, also called friendly fraud, happens when a customer receives their order and then disputes the charge with their bank. The platform loses the order value and pays a chargeback fee on top.
Refund abuse happens inside the app. A customer repeatedly reports missing items, cold food, or non-delivery to collect credits or refunds. Because in-app refunds are fast and low-friction by design, this can cost more in total than chargebacks.
The difficulty is that genuine complaints and fraudulent ones look identical at the transaction level. A single claim rarely tells you much. History does: how often this account, and other accounts on the same device, have claimed refunds before. Linking claims back to the device helps teams spot serial abusers who rotate accounts, without adding friction for customers with a real complaint.
Fake Account Fraud
Fake accounts are the entry point for most types of food delivery fraud. Fraudsters use them to evade platform bans, game referral systems, and build a base for larger coordinated attacks.
The challenge with fake account detection in food delivery is that each account, in isolation, can look entirely legitimate. The signal is at the device level — multiple accounts originating from the same physical device — which is why fake account detection in food delivery requires device-level identification rather than identity checks alone.
Driver Fraud
Driver-side fraud covers a range of behaviors: account sharing, where unvetted individuals make deliveries under another driver's verified profile; automated order acceptance using bots to monopolize order queues; and ghost orders, where drivers mark deliveries as complete without ever fulfilling them.
For platforms, driver fraud creates real operational risk. When unverified individuals are on the road under a trusted driver's identity, the platform loses visibility into who is actually interacting with customers.
GPS Spoofing
GPS spoofing allows drivers to manipulate the location data reported by their device to the platform. In practice, this means a driver can appear to be near a restaurant when they are across town, claim higher-distance payout bonuses without covering the actual distance, or mark an order as delivered without ever reaching the customer.
Platforms that rely solely on GPS data to verify delivery completion are especially exposed. Detecting spoofing requires identifying the tools used to manipulate location data at the device level, not just cross-checking coordinates.
Ghost Orders (Bot-Driven Fake Orders)
This is the most automated form of food delivery fraud. Here, ghost orders means fabricated orders where the fraudster controls both sides of the transaction.
Using app cloners and emulators, the fraudster runs fake customer and courier accounts on the same device or a small device farm. Autoclickers accept the orders, and GPS spoofers simulate the delivery route.
The result is a complete order lifecycle that exists only on paper. No food moves, but the fake order still triggers courier incentives, referral rewards, or promotional credit. At scale, this kind of incentive fraud can drain a growth budget quickly.
Collusion Fraud
Collusion happens when two parties on the platform work together to defraud it.
A customer and courier might agree to mark an order as undelivered, collect the refund, and split it. A restaurant might place fake orders with itself to boost its ranking or claim platform-funded promotions. A courier and a merchant might cooperate to inflate order values or incentive payouts.
Collusion is hard to see because each participant looks like a normal user. The connection often shows up at the device level, in customer, courier, and merchant accounts that share devices or repeatedly transact with each other in unusual patterns.
How Bot Attacks Affect Food Delivery Platforms
Bots operate faster than any manual review can catch. By the time a fraud team flags the activity, the damage is done. Here is what bot attacks actually look like on a food delivery platform:
Flood platforms with fake account registrations at scale
Drain promotional budgets within minutes of a campaign going live
Monopolize order queues, locking out legitimate drivers
Simulate full order lifecycles to trigger unearned driver incentives
Why bot attacks in food delivery platforms are hard to catch
Each bot-generated account looks legitimate in isolation
Attacks happen in real time, faster than rule-based systems respond
Fraudsters rotate devices and identities to avoid pattern detection
Effective bot detection tools for restaurant delivery platforms need to work at the device and session level, identifying the tools behind the attack rather than reacting to its outcome.
How Food Delivery Apps Prevent Multi-Accounting
Multi-accounting is hard to catch at the identity layer because fraudsters use different emails, phone numbers, and payment methods for each account. The reliable signal is the device, not the user.
Where traditional methods in food delivery fall short
Email and phone verification are easily bypassed with disposable credentials
IP-based detection fails when fraudsters use VPNs or proxies
Behavioral rules alone cannot link accounts created days or weeks apart
What actually works
Persistent device identification that survives app reinstalls and factory resets
Linking multiple accounts back to a single physical device
Flagging devices already associated with banned accounts before a new one is approved
Stopping multi-accounting requires identifying the device behind the account, not just the credentials on top of it.
How Real-Time Fraud Detection Works in Food Delivery Apps
Rule-based fraud detection reacts to patterns it has already seen. Real-time fraud detection catches threats as they unfold, even new ones. Here is how it works in practice:
On the very first interaction, every device is assigned a persistent identifier the moment it touches the platform
Devices linked to previously banned accounts are flagged before a new account is approved
Emulators and app cloners are detected at the point of registration
What Makes A Difference?
Device behavior is monitored continuously throughout the session, not just at login
The moment a malicious tool activates, such as a GPS spoofer or autoclicker, it is flagged in real time
A trust score is updated dynamically based on live session signals
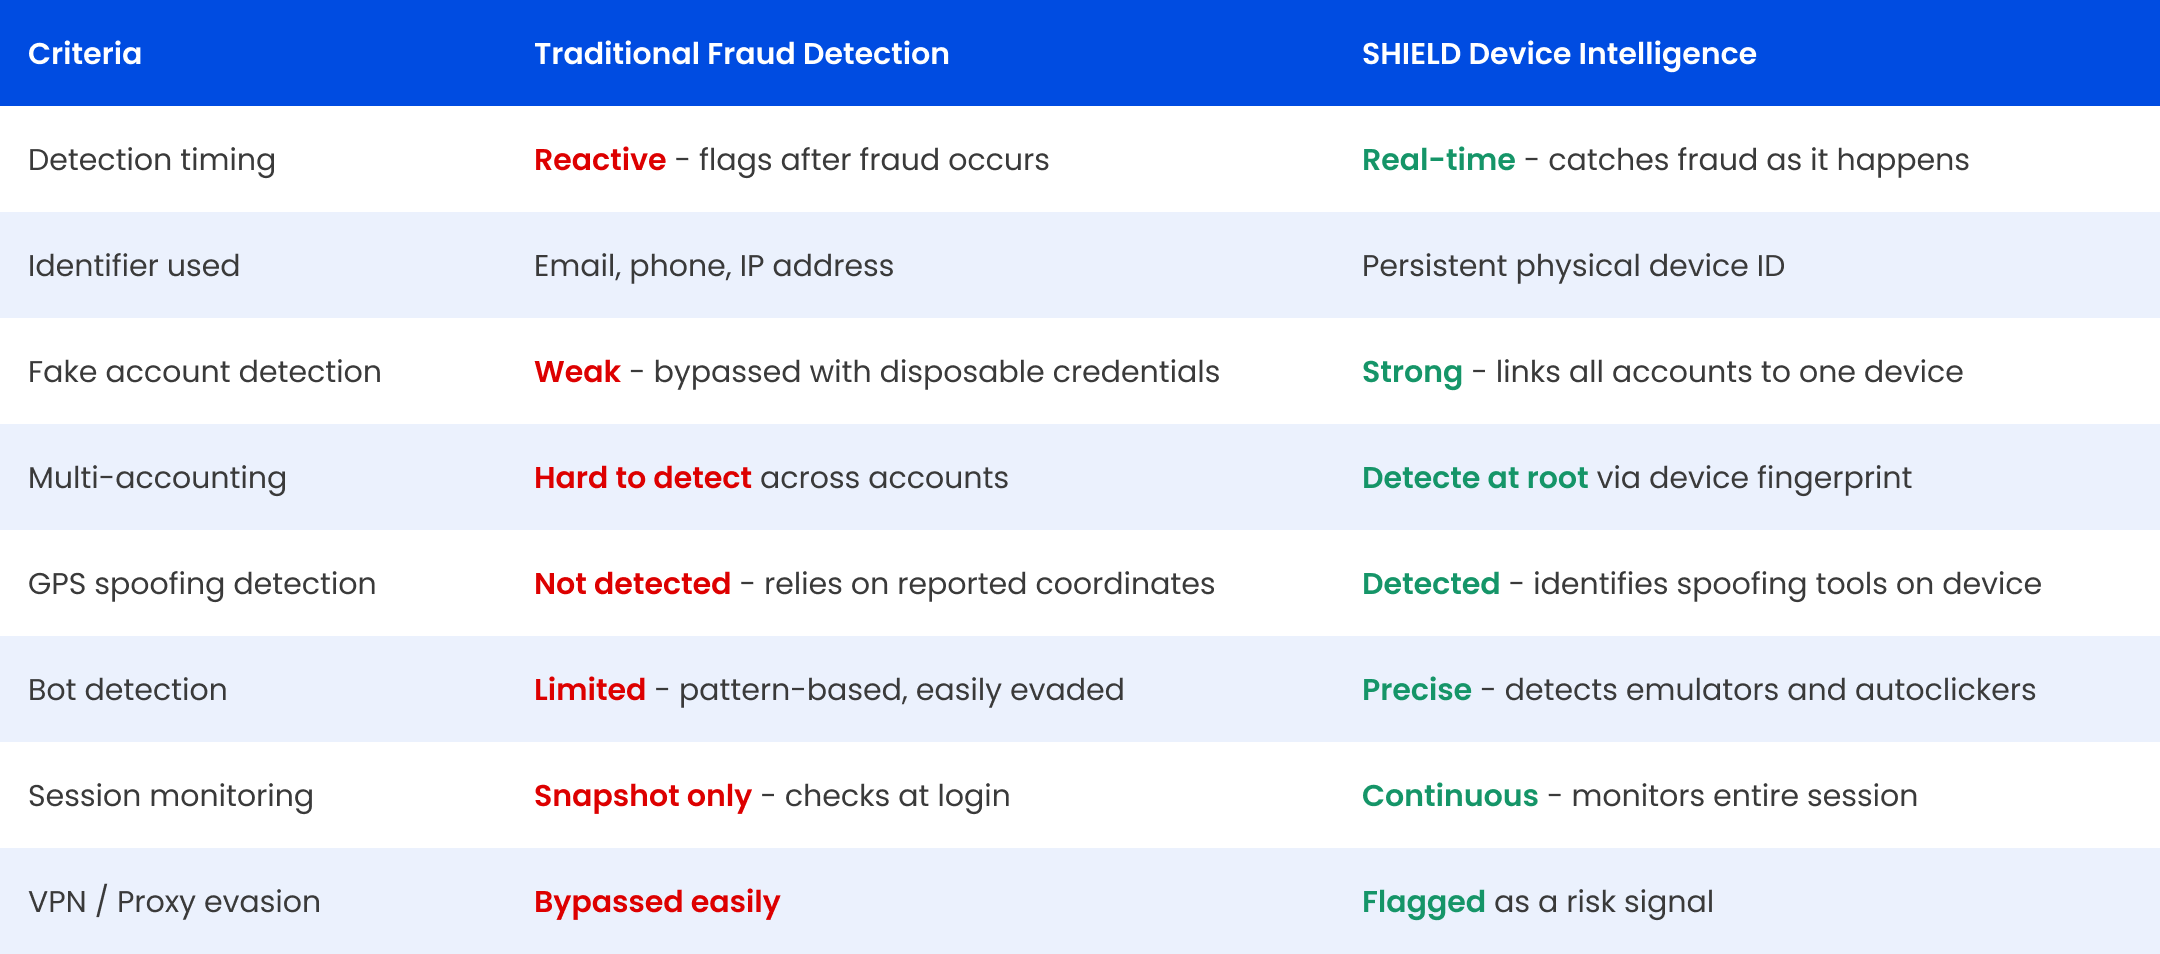
The key difference from traditional approaches is continuity. Fraud does not always begin at login. A legitimate user can turn fraudulent mid-session, and real-time detection is the only way to catch that shift before damage is done.
Device Intelligence vs Traditional Fraud Detection
Conclusion
Food delivery fraud is not a single problem with a single fix. It spans fake accounts, bot attacks, GPS spoofing, promo abuse, and chargeback fraud, often running simultaneously across the customer and driver sides of the same platform.
What ties every effective defense together is working at the device level. Credentials can be faked, IPs can be masked, and identities can be spoofed, but every fraudster needs a physical device. That is where prevention has to start.
Detecting and Preventing Food Delivery Fraud with SHIELD
SHIELD is a device intelligence for enterprises trusted by global platforms including inDrive and Snoonu to eliminate fake accounts and all fraudulent activity.
SHIELD Device ID
Uniquely identifies every physical device on your platform with over 99.99% accuracy
Persists across app reinstalls, factory resets, and device fingerprint changes
Links multiple accounts back to a single device, stopping multi-accounting and fake account fraud at the root
SHIELD Fraud Intelligence
Continuously monitors every device session through SHIELD Sentinel, the only always-on session monitoring in the industry
Detects over 20 malicious tools in real time including GPS spoofers, app cloners, emulators, and autoclickers
Identifies the exact moment a trusted user turns fraudulent, mid-session, before damage occurs
Returns a live Trust Score per device, giving your risk team an at-a-glance signal for every user on the platform
Why food delivery platforms choose SHIELD
Covers 231+ countries through a continuously updated Global Intelligence Network
No PII required, fully GDPR compliant and SOC 2 certified
Plug-and-play SDK for iOS, Android, and web with no additional code needed
SHIELD gives food delivery platforms the device-level visibility needed to stop fraud before it scales, without adding friction for legitimate users.
FAQs
What is food delivery fraud?
Food delivery fraud is any deliberate attempt by customers, drivers, or organized fraud rings to exploit a food delivery platform for financial gain — through fake accounts, false refund claims, GPS spoofing, or bot-driven order manipulation.
How do food delivery apps detect fraud?
Leading platforms use device-level fraud detection to catch threats in real time. Key methods include:
Persistent device identification across sessions and reinstalls
Real-time detection of malicious tools like GPS spoofers and emulators
Continuous session monitoring to catch mid-session fraud
Trust scoring to assess device risk at a glance
What are bot attacks in food delivery apps?
Bot attacks use automated scripts to create fake accounts, drain promotions, monopolize order queues, and simulate deliveries — all without any real human interaction. They are fast, scalable, and invisible to rule-based systems.
How can platforms prevent fake accounts?
Effective fake account prevention requires:
Identifying every device with a persistent device ID
Linking new accounts to previously banned devices before approval
Detecting emulators and app cloners at the point of registration
What is chargeback fraud in food delivery?
Chargeback fraud, also called friendly fraud, happens when a customer receives their order and then disputes the charge with their bank. Effective chargeback management for food delivery platforms relies on building behavioral context around each user to separate genuine disputes from abuse.
How does device intelligence help prevent fraud?
Device intelligence fraud detection works by identifying the physical device behind every account and action. It detects spoofed devices, malicious tools, and multi-accounting at the root — before fraud causes damage — rather than reacting after the fact.
Why is real-time fraud detection important for food delivery apps?
Because fraud does not wait. Real-time fraud detection in food delivery catches threats mid-session — the moment a GPS spoofer activates or a bot accepts an order — stopping the attack before the platform absorbs the loss.
Ready to safeguard your food delivery platform from fraud? Discover how SHIELD can help